Showing posts with label updates. Show all posts
Showing posts with label updates. Show all posts
Thursday, April 13, 2017
New Adobe CRITICAL Security Updates Acrobat Pro and Reader 11 0 03
New Adobe CRITICAL Security Updates Acrobat Pro and Reader 11 0 03
-
[Updated 2013-05-21 @8:38 AM: I removed the paragraphs and image regarding a low resolution icon for Adobe Reader. What I had witnessed was, I have discovered, yet another bug in Apples Finder application. Ive witnessed the exact same phenomenon with other newly installed apps. Refreshing or relaunching the Finder removes the problem. Not good Apple! Apologies to Adobe.]
On schedule, Adobe has posted critical security updates of both Acrobat Pro and Reader. The download links are below.
Thankfully, Adobe has (belatedly) provided an updated Security Bulletin as well, which is also linked below. The updates patch 27 security vulnerabilities.
Security Bulletin:
http://www.adobe.com/support/security/bulletins/apsb13-15.html
Adobe Reader XI (11.0.03):
http://get2.adobe.com/reader/
Adobe Acrobat Pro XI (11.0.03):
http://www.macupdate.com/download/1833/AcrobatUpd11003.dmg
Here are the security CVE vulnerabilities patched by these updates:
These updates resolve memory corruption vulnerabilities that could lead to code execution (CVE-2013-2718, CVE-2013-2719, CVE-2013-2720, CVE-2013-2721, CVE-2013-2722, CVE-2013-2723, CVE-2013-2725, CVE-2013-2726, CVE-2013-2731, CVE-2013-2732, CVE-2013-2734, CVE-2013-2735, CVE-2013-2736, CVE-2013-3337, CVE-2013-3338, CVE-2013-3339, CVE-2013-3340, CVE-2013-3341).
These updates resolve an integer underflow vulnerability that could lead to code execution (CVE-2013-2549).
These updates resolve a use-after-free vulnerability that could lead to a bypass of Adobe Readers sandbox protection (CVE-2013-2550).
These updates resolve an information leakage issue involving a Javascript API (CVE-2013-2737).
These updates resolve a stack overflow vulnerability that could lead to code execution (CVE-2013-2724).
These updates resolve buffer overflow vulnerabilities that could lead to code execution (CVE-2013-2730, CVE-2013-2733).
These updates resolve integer overflow vulnerabilities that could lead to code execution (CVE-2013-2727, CVE-2013-2729).
These updates resolve a flaw in the way Reader handles domains that have been blacklisted in the operating system (CVE-2013-3342).

--
Go to link Download

Sunday, February 26, 2017
Oracle Java Quarterly Security Updates July 2015
Oracle Java Quarterly Security Updates July 2015

Oracle released the scheduled critical security updates for its Java SE Runtime Environment software.
Unwanted "Extras"
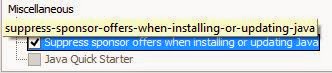
Although most people do not need Java on their computer, there are some programs and games that require Java. In the event you need to continue using Java, How-to Geek discovered a little-known and unpublicized option in the Java Control Panel to suppress the offers for the pre-checked unwanted extras that Oracle has long included with the updates. Although the Ask Toolbar has been removed, tha does not preclude the pre-checked option for some other unnecessary add-on.Do the following to suppress the sponsor offers:
- Launch the Windows Start menu
- Click on Programs
- Find the Java program listing
- Click Configure Java to launch the Java Control Panel
- Click the Advanced tab and go to the "Miscellaneous" section at the bottom.
- Check the box by the “Suppress sponsor offers when installing or updating Java” option and click OK.
Windows XP
For information on Java support for Windows XP, organizations and individuals who must continue using Windows XP and have Java installed are referred to the Oracle blog post, The future of Java on Windows XP (Henrik on Java).Update
If Java is still installed on your computer, it is recommended that this update be applied as soon as possible due to the threat posed by a successful attack.Download Information
Download link: Java SE 8u51Verify your version: http://www.java.com/en/download/testjava.jsp
Notes:
- UNcheck any pre-checked toolbar and/or software options presented with the update. They are not part of the software update and are completely optional.
- Starting with Java SE 7 Update 21 in April 2013, all Java Applets and Web Start Applications should be signed with a trusted certificate. It is not recommended to run untrusted/unsigned Certificates. See How to protect your computer against dangerous Java Applets
Critical Patch Updates
For Oracle Java SE Critical Patch Updates, the next scheduled dates are as follows:- 20 October 2015
- 19 January 2016
- 19 April 2016
Java Security Recommendations
For those people who have desktop applications that require Java and cannot uninstall it, Java can now be disabled in Internet Explorer. See Microsoft Fix it to Disable Java in Internet Explorer.1) In the Java Control Panel, at minimum, set the security to high.
2) Keep Java disabled until needed. Uncheck the box "Enable Java content in the browser" in the Java Control Panel.

3) If you use Firefox or Pale Moon, install NoScript and only allow Java on those sites where it is required.
Instructions on removing older (and less secure) versions of Java can be found at http://java.com/en/download/faq/remove_olderversions.xml
References
- Java SE 8 Update Release Notes
- Java, The Never-Ending Saga
- Oracle Quality Assurance Blog
- Critical Patch Updates and Security Alerts

Remember - "A day without laughter is a day wasted."
May the wind sing to you and the sun rise in your heart...
Go to link Download
Thursday, January 19, 2017
Nokia introduces two new updates for Symbian Anna
Nokia introduces two new updates for Symbian Anna
Nokia expands the online version of Nokia Maps
Now that the most current Nokia devices with Symbian ^ 3 should have had the benefit of the Anna updates, Nokia will begin now with the provision of two new updates. Firstly, this is a so-called Service Pack and the Second is an update to the version of Symbian Anna v25.
The Service Pack is mainly according to Nokia, as well as improvements in performance when scrolling through text messages. If the user wants to provide his photos with geotags, the GPS information to the service pack is also available significantly faster. The Service Pack can be carried out via the Nokia Suite, Nokia Software Updater or directly through the menu-point update on the smartphone. The installation file is about 700 KB in size and could be installed easily on our Nokia N8. After installation, the device will be rebooted, but still has all the settings, appointments and contacts.
The update, which is just under 1 MB in size, for Symbian Anna on the other hand, version 25 brings fixes primarily for internal functions of the operating system. For more information about changes to had not yet been put in experience, especially since the update for our Nokia N8 to date not yet available. When the various devices, the software version v25 will receive is always dependent on how you update the firmware on factors such as network operators, product code and branding, especially since the various providers, the firmware first test and possibly adapt to their smartphones. Unfortunately, the press department of Nokia could give no further information on this yet. Both updates, both the service pack and the firmware update will be available for the current device with Symbian ^ 3/Anna. As always with firmware updates, nor the obligatory reference to ensure all personal data before installation.
Nokia Maps for Android, iOS and Co.
For some time, is one of Nokia Maps web app available to assist with web browsers that support HTML5, can be used. Until now, the functionality, as we reported in a message, still quite strong and restricted to devices with Android or iOS no real competitor to Google Maps. Meanwhile, Nokia has the web app of maps but also further developed and equipped with new functions, which is approaching the functionality of the navigation software from Google. It is now possible in addition to the route guidance, including information on public transportation and off-line use of the map. Here, the off-line feature as with Google Maps for Android will be realized in that the user need, map it on his smartphone via WLAN invites.
In July of this year we also reported in a message on the revised web version of Nokia Maps and its new features. How Nokia is now reporting on his blog Conversations by Nokia, the functionality has been further extended. So it is now possible, at least for users of Google Chrome, the 3D view without additional browser plug-in to use, with other browsers currently require a plug-in. According to Nokia the alternative Internet browser, however, are in the testing phase. Furthermore, were the so-called heat maps to 56 cities, worldwide. With these cards, the user receives an overview of problems regarding attractions, nightlife or shopping in a foreign city. The possibility to obtain information on public transport and to be thereby creating routes from A to B has been expanded. Thus, the route planning for a total of 420 cities is available in 30 cities are also detailed timetable information available.
Go to link Download
Monday, December 12, 2016
On Vacation but Java updates from Oracle and Apple Be sure to have the UNmessed up Apple Java update!!! and Adobe Flash Update
On Vacation but Java updates from Oracle and Apple Be sure to have the UNmessed up Apple Java update!!! and Adobe Flash Update
--

Im on a break while I work on other things. But here is some quickie news. I expect, if youre a regular reader, you know how to dig up the URLs and CVE reports by now.
I) MASSIVE CRITICAL Java update from both Oracle and Apple, including 40 (FORTY) security patches. Apples update is for Java version 1.6 only, the part of Java included in OS X. The update is for OS X 10.6 - 10.8.
II) Apple MESSED-UP their original Java update release, which was labeled "JavaForOSX2013-003". This mess KILLED Java and must be updated with what replaced it: "JavaForOSX2013-004". From my experience, Software Update did NOT provide me with the updated version. I had to grab oo4 myself and apply it myself. You may have to do so as well.
Here is an article to help you sort out whether you got STUNG by Apples mess or not, and how to clean it up. Thank you to 9to5Mac.com:
Bug in Apple Java update – now fixed, but check you have the correct version
III) Adobe tossed out a scheduled Flash update that patched one critical security hole. If you use Flash any more, be sure you have applied this latest update.
OTHER AMUSING NEWS:
Im running into hilarious FUD about the MacKeeper crapware from none other than one of their competitors. They claim you can REMOVE crappy MacKeeper by installing THEIR crappy software instead. Needless to say, avoid replacing crap with crap. If you foolishly installed MacKeeper, go to their website to learn how to UNinstall it.
Also amusing: Apparently crappy MacKeeper has been sold to some other company, who apparently have changed none of crappy ZeoBITs evil marketing moron tactics. But at least it is good to know that everyones efforts to kick ZeoBIT in the dangly bits has been successful. ZeoBIT is now out of the picture, hurray. Lets hope their crapware is soon to follow.

Also note: There has been a rash of Microsoft Office specific malware. I personally dont care or follow such malware. Youre on your own if you still put up with Microsoft. But its worth noting that Office malware continues. Check out my net buddy Thomas Reeds The Safe Mac security blog for details. I believe Intego and Sophos have been following this scourge as well. Links to their sites are on the right of this page.
Enjoy the summer!
Stay cool.
Stay kewl.
:-Derek

Go to link Download
Thursday, November 10, 2016
Offline NokiFirm Latest Version Free Download All Updates
Offline NokiFirm Latest Version Free Download All Updates
NokiFirm Offline Installer v17.0, v18.0, and v19.0
Download NokiFirm latest version offline installer for windows here. On this page I have brought you nokifirm all updates to free download. You will be able to download nokifirm offline installers of verion v17.0, version v18.0, and version v19.0 full from an open source. Because I have brought you the direct downloading links from various open sources of the last three version of nokifirm. The nokifirm v17.0 offline file setup can be free download from the below of this post. The other two versions of nokifirm offline setups v18.0 and v19.0 can also be downloaded free from the bottom of this page.

How to Download?
- Download nokifirm 17.0, v18.0 and v19.0 download at the bottom
- Wait to be completed the downloading process
- Extract if in zip form
- Double click on the given downloaded file to start installation
- Follow the instructions that will be on your screen
- And finished to complete the installation
To start downloading of offline nokifirm versions, you have to choose the accurate version downloading from here to download the nokifirm version v17.0 or v18.0 or v19.0 full file. You can also download all the given version files from here. There is not any prohibition rules about the downloading. Nokifirm v19.0 not available to download at this time. So, choose the link and get start to your needed version file from the remaining two.
Nokifirm v17.0
Nokifirm v18.0
Go to link Download
Tuesday, October 18, 2016
OS X 10 10 2 Yosemite Safari Updates and Security Update 2015 001 From Apple 58 New Security Patches
OS X 10 10 2 Yosemite Safari Updates and Security Update 2015 001 From Apple 58 New Security Patches
--

[Update: The link to Apples security document for 10.10.2 & 2015-001 has be added below.]Apple has released the latest OS X update to OS X 10.10.2 Yosemite as well as Security Update 2015-001. Included with these updates are new updates of Safari with its own security patches. There is a total of 58 new security patches. You can obtain the updates via the Updates tab in the App Store application or eventually at:
http://www.apple.com/support/downloads/
Below, I have provided the full Apple security documents for 10.10.2, Security Update 2015-001 and Safari. You can also access them at Apples website:
The security content document for OS X 10.10.2 Yosemite as well as Security Update 2015-001 can be found at:
http://support.apple.com/en-us/HT204244
The security content document for Safari 8.0.3, 7.1.3 and 6.2.3 is available at:
https://support.apple.com/kb/HT204243
Ive highlighted at the CVE numbers in Apples OS X 10.10.2 security document. (CVE = Common Vulnerabilities and Exposures). If youd like more information about any of the CVEs, use the link on the right of this page marked CVE Search. It will take you to the search page at Mitre.org. If you cant find a specific CVE there or the CVE has no description, it is because the developer of the affected software has requested that the CVE information not yet be made public.
~ ~ ~ ~ ~
APPLE-SA-2015-01-27-4
OS X 10.10.2 and Security Update 2015-001
Available for: OS X Mavericks v10.9.5
Impact: A remote attacker may be able to determine all the network addresses of the system
Description: The AFP file server supported a command which returned all the network addresses of the system. This issue was addressed by removing the addresses from the result.
CVE-ID
CVE-2014-4426 : Craig Young of Tripwire VERT
Available for: OS X Yosemite v10.10 and v10.10.1
Impact: Multiple vulnerabilities in bash, including one that may allow local attackers to execute arbitrary code
Description: Multiple vulnerabilities existed in bash. These issues were addressed by updating bash to patch level 57.
CVE-ID
CVE-2014-6277
CVE-2014-7186
CVE-2014-7187
Available for: OS X Mountain Lion v10.8.5, OS X Mavericks v10.9.5
Impact: A malicious application may be able to execute arbitrary code with system privileges
Description: An integer signedness error existed in IOBluetoothFamily which allowed manipulation of kernel memory. This issue was addressed through improved bounds checking. This issue does not affect OS X Yosemite systems.
CVE-ID
CVE-2014-4497
Available for: OS X Yosemite v10.10 and v10.10.1
Impact: A malicious application may be able to execute arbitrary code with system privileges
Description: An error existed in the Bluetooth driver that allowed a malicious application to control the size of a write to kernel memory. The issue was addressed through additional input validation.
CVE-ID
CVE-2014-8836 : Ian Beer of Google Project Zero
Available for: OS X Yosemite v10.10 and v10.10.1
Impact: A malicious application may be able to execute arbitrary code with system privileges
Description: Multiple security issues existed in the Bluetooth driver, allowing a malicious application to execute arbitrary code with system privilege. The issues were addressed through additional input validation.
CVE-ID
CVE-2014-8837 : Roberto Paleari and Aristide Fattori of Emaze Networks
Available for: OS X Yosemite v10.10 and v10.10.1
Impact: Website cache may not be fully cleared after leaving private browsing
Description: A privacy issue existed where browsing data could remain in the cache after leaving private browsing. This issue was addressed through a change in caching behavior. CVE-ID
CVE-2014-4460
Available for: OS X Mountain Lion v10.8.5, OS X Mavericks v10.9.5, OS X Yosemite v10.10 and v10.10.1
Impact: Opening a maliciously crafted PDF file may lead to an unexpected application termination or arbitrary code execution
Description: An integer overflow existed in the handling of PDF files. This issue was addressed through improved bounds checking.
CVE-ID
CVE-2014-4481 : Felipe Andres Manzano of the Binamuse VRT, via the iSIGHT Partners GVP Program
Available for: OS X Yosemite v10.10 and v10.10.1, for: MacBook Pro Retina, MacBook Air (Mid 2013 and later), iMac (Late 2013 and later), Mac Pro (Late 2013)
Impact: A malicious Thunderbolt device may be able to affect firmware flashing
Description: Thunderbolt devices could modify the host firmware if connected during an EFI update. This issue was addressed by not loading option ROMs during updates.
CVE-ID
CVE-2014-4498 : Trammell Hudson of Two Sigma Investments
Available for: OS X Yosemite v10.10 and v10.10.1
Impact: An attacker with access to a system may be able to recover Apple ID credentials
Description: An issue existed in the handling of App Store logs. The App Store process could log Apple ID credentials in the log when additional logging was enabled. This issue was addressed by disallowing logging of credentials.
CVE-ID
CVE-2014-4499 : Sten Petersen
Available for: OS X Yosemite v10.10 and v10.10.1
Impact: Some third-party applications with non-secure text entry and mouse events may log those events
Description: Due to the combination of an uninitialized variable and an applications custom allocator, non-secure text entry and mouse events may have been logged. This issue was addressed by ensuring that logging is off by default. This issue did not affect systems prior to OS X Yosemite.
CVE-ID
CVE-2014-1595 : Steven Michaud of Mozilla working with Kent Howard
Available for: OS X Mountain Lion v10.8.5, OS X Mavericks v10.9.5
Impact: Opening a maliciously crafted PDF file may lead to an unexpected application termination or arbitrary code execution
Description: A memory corruption issue existed in the handling of PDF files. The issue was addressed through improved bounds checking. This issue does not affect OS X Yosemite systems.
CVE-ID
CVE-2014-8816 : Mike Myers, of Digital Operatives LLC
Available for: OS X Mountain Lion v10.8.5, OS X Mavericks v10.9.5, OS X Yosemite v10.10 and v10.10.1
Impact: A malicious application may be able to execute arbitrary code with system privileges
Description: Multiple type confusion issues existed in coresymbolicationds handling of XPC messages. These issues were addressed through improved type checking.
CVE-ID
CVE-2014-8817 : Ian Beer of Google Project Zero
Available for: OS X Mountain Lion v10.8.5, OS X Mavericks v10.9.5, OS X Yosemite v10.10 and v10.10.1
Impact: Processing a maliciously crafted .dfont file may lead to an unexpected application termination or arbitrary code execution
Description: A memory corruption issue existed in the handling of .dfont files. This issue was addressed through improved bounds checking.
CVE-ID
CVE-2014-4484 : Gaurav Baruah working with HPs Zero Day Initiative
Available for: OS X Mountain Lion v10.8.5, OS X Mavericks v10.9.5, OS X Yosemite v10.10 and v10.10.1
Impact: Opening a maliciously crafted PDF file may lead to an unexpected application termination or arbitrary code execution
Description: A buffer overflow existed in the handling of font files. This issue was addressed through improved bounds checking.
CVE-ID
CVE-2014-4483 : Apple
Available for: OS X Mavericks v10.9.5, OS X Yosemite v10.10 and v10.10.1
Impact: Viewing a maliciously crafted XML file may lead to an unexpected application termination or arbitrary code execution
Description: A buffer overflow existed in the XML parser. This issue was addressed through improved bounds checking.
CVE-ID
CVE-2014-4485 : Apple
Available for: OS X Mountain Lion v10.8.5, OS X Mavericks v10.9.5, OS X Yosemite v10.10 and v10.10.1
Impact: Multiple vulnerabilities in Intel graphics driver
Description: Multiple vulnerabilities existed in the Intel graphics driver, the most serious of which may have led to arbitrary code execution with system privileges. This update addresses the issues through additional bounds checks.
CVE-ID
CVE-2014-8819 : Ian Beer of Google Project Zero CVE-2014-8820 : Ian Beer of Google Project Zero
CVE-2014-8821 : Ian Beer of Google Project Zero
Available for: OS X Mountain Lion v10.8.5, OS X Mavericks v10.9.5, OS X Yosemite v10.10 and v10.10.1
Impact: A malicious application may be able to execute arbitrary code with system privileges
Description: A null pointer dereference existed in IOAcceleratorFamilys handling of certain IOService userclient types. This issue was addressed through improved validation of IOAcceleratorFamily contexts.
CVE-ID
CVE-2014-4486 : Ian Beer of Google Project Zero
Available for: OS X Mountain Lion v10.8.5, OS X Mavericks v10.9.5, OS X Yosemite v10.10 and v10.10.1
Impact: A malicious application may be able to execute arbitrary code with system privileges
Description: A buffer overflow existed in IOHIDFamily. This issue was addressed with improved bounds checking.
CVE-ID
CVE-2014-4487 : TaiG Jailbreak Team
Available for: OS X Mountain Lion v10.8.5, OS X Mavericks v10.9.5, OS X Yosemite v10.10 and v10.10.1
Impact: A malicious application may be able to execute arbitrary code with system privileges
Description: A validation issue existed in IOHIDFamilys handling of resource queue metadata. This issue was addressed through improved validation of metadata.
CVE-ID
CVE-2014-4488 : Apple
Available for: OS X Mountain Lion v10.8.5, OS X Mavericks v10.9.5, OS X Yosemite v10.10 and v10.10.1
Impact: A malicious application may be able to execute arbitrary code with system privileges
Description: A null pointer dereference existed in IOHIDFamilys handling of event queues. This issue was addressed through improved validation of IOHIDFamily event queue initialization.
CVE-ID
CVE-2014-4489 : @beist
Available for: OS X Mountain Lion v10.8.5, OS X Mavericks v10.9.5, OS X Yosemite v10.10 and v10.10.1
Impact: Executing a malicious application may result in arbitrary code execution within the kernel
Description: A bounds checking issue existed in a user client vended by the IOHIDFamily driver which allowed a malicious application to overwrite arbitrary portions of the kernel address space. The issue is addressed by removing the vulnerable user client method.
CVE-ID
CVE-2014-8822 : Vitaliy Toropov working with HPs Zero Day Initiative
Available for: OS X Yosemite v10.10 and v10.10.1
Impact: A malicious application may be able to execute arbitrary code with system privileges
Description: An integer overflow existed in the handling of IOKit functions. This issue was addressed through improved validation of IOKit API arguments.
CVE-ID
CVE-2014-4389 : Ian Beer of Google Project Zero
Available for: OS X Yosemite v10.10 and v10.10.1
Impact: A privileged application may be able to read arbitrary data from kernel memory
Description: A memory access issue existed in the handling of IOUSB controller user client functions. This issue was addressed through improved argument validation.
CVE-ID
CVE-2014-8823 : Ian Beer of Google Project Zero
Available for: OS X Mountain Lion v10.8.5, OS X Mavericks v10.9.5, OS X Yosemite v10.10 and v10.10.1
Impact: A malicious application may be able to execute arbitrary code with system privileges
Description: Specifying a custom cache mode allowed writing to kernel read-only shared memory segments. This issue was addressed by not granting write permissions as a side-effect of some custom cache modes.
CVE-ID
CVE-2014-4495 : Ian Beer of Google Project Zero
Available for: OS X Mountain Lion v10.8.5, OS X Mavericks v10.9.5, OS X Yosemite v10.10 and v10.10.1
Impact: A malicious application may be able to execute arbitrary code with system privileges
Description: A validation issue existed in the handling of certain metadata fields of IODataQueue objects. This issue was addressed through improved validation of metadata. CVE-ID
CVE-2014-8824 : @PanguTeam
Available for: OS X Yosemite v10.10 and v10.10.1
Impact: A local attacker can spoof directory service responses to the kernel, elevate privileges, or gain kernel execution Description: Issues existed in identitysvc validation of the directory service resolving process, flag handling, and error handling. This issue was addressed through improved validation.
CVE-ID
CVE-2014-8825 : Alex Radocea of CrowdStrike
Available for: OS X Yosemite v10.10 and v10.10.1
Impact: A local user may be able to determine kernel memory layout
Description: Multiple uninitialized memory issues existed in the network statistics interface, which led to the disclosure of kernel memory content. This issue was addressed through additional memory initialization.
CVE-ID
CVE-2014-4371 : Fermin J. Serna of the Google Security Team
CVE-2014-4419 : Fermin J. Serna of the Google Security Team
CVE-2014-4420 : Fermin J. Serna of the Google Security Team
CVE-2014-4421 : Fermin J. Serna of the Google Security Team
Available for: OS X Mavericks v10.9.5
Impact: A person with a privileged network position may cause a denial of service
Description: A race condition issue existed in the handling of IPv6 packets. This issue was addressed through improved lock state checking.
CVE-ID
CVE-2011-2391
Available for: OS X Mountain Lion v10.8.5, OS X Mavericks v10.9.5, OS X Yosemite v10.10 and v10.10.1
Impact: Maliciously crafted or compromised applications may be able to determine addresses in the kernel
Description: An information disclosure issue existed in the han
Go to link Download
Subscribe to:
Posts (Atom)