Monday, May 15, 2017
Norton Internet Security 2014 CRACK with Keygen
Norton Internet Security 2014 CRACK with Keygen

Do not be afraid to miss something, because we are always on guard of your security - SONAR technology and components clock monitoring monitor suspicious transactions on your computer and quickly identify threats.
Load whatever you want - our remedies scan downloaded files and eliminate threats found.
Perform deep cleaning computer - our effective removal function eliminates threats from even the most complex in terms of the elimination of threats that are often overlooked by simpler products.
Use global protection - only Norton creates super-efficient network protection, blocking most threats before they reach your computer.
Securing the future, available today - our exclusive technology to protect against viruses, based on analysis of behavior and reputation, able to stop online threats that have not even invented by hackers.
Stay away from intruders - Browser protection function blocks unsafe websites that without your knowledge download software to steal confidential information or gain control over your computer.
Reflect any attempt identity theft - is the only way to shop, browse the web and use social networks without worrying about the consequences.
In order to get to a fraudulent website, enough to make one wrong move, but our protection block phishing websites that tricked you to reveal your passwords, credit card numbers or other sensitive information.
Links on Facebook are a great temptation - now you do not need to worry about whether the news Facebook links to fraudulent sites or dangerous downloads.
Protects identity by securely storing and automatically enter user names and passwords.

Downloads: | Updated: | File type: RAR
crack file free download licence 2014 crack free download osx crack only "registration key" crack with serial key "serial number" "license key" x86 pc crack full 2014 serial key and crack serial number bit serial key patch ita 2010 windows crack windows 8 serial key free crack patch "license key list" x64 Norton Internet Security 2014 keygen 2013 "full patch" crack lifetime gratuit crack and serial key windows francais serial key "crack keygen download free" "download with serial key and crack" 2012 product window telecharger crack download download crack full version mac
Go to link Download

Wednesday, May 10, 2017
Oracle Java Quarterly Critical Security Update January 2016
Oracle Java Quarterly Critical Security Update January 2016

Oracle released the scheduled critical security updates for its Java SE Runtime Environment software and, once again, released a subsequent update that includes "bug fixes".
Unwanted "Extras"
Although most people do not need Java on their computer, there are some programs and games that require Java. In the event you need to continue using Java, How-to Geek discovered a little-known and unpublicized option in the Java Control Panel to suppress the offers for the pre-checked unwanted extras that Oracle has long included with the updates. Although the Ask Toolbar has been removed, tha does not preclude the pre-checked option for some other unnecessary add-on.Do the following to suppress the sponsor offers:
- Launch the Windows Start menu
- Click on Programs
- Find the Java program listing
- Click Configure Java to launch the Java Control Panel
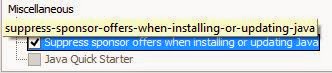
- Click the Advanced tab and go to the "Miscellaneous" section at the bottom.
- Check the box by the “Suppress sponsor offers when installing or updating Java” option and click OK.
Windows XP
For information on Java support for Windows XP, organizations and individuals who must continue using Windows XP and have Java installed are referred to the Oracle blog post, The future of Java on Windows XP (Henrik on Java).Update
If Java is still installed on your computer, it is recommended that this update be applied as soon as possible due to the threat posed by a successful attack.Download Information
Download link: Java SE 8u71Java SE 8u72 can be found here. Select the appropriate version for your operating system.
Verify your version: http://www.java.com/en/download/testjava.jsp
Notes:
- UNcheck any pre-checked toolbar and/or software options presented with the update. They are not part of the software update and are completely optional.
- Starting with Java SE 7 Update 21 in April 2013, all Java Applets and Web Start Applications should be signed with a trusted certificate. It is not recommended to run untrusted/unsigned Certificates. See How to protect your computer against dangerous Java Applets
Critical Patch Updates
For Oracle Java SE Critical Patch Updates, the next scheduled dates are as follows:- 19 April 2016
- 19 July 2016
- 18 October 2016
- 17 January 2017
Java Security Recommendations
For those people who have desktop applications that require Java and cannot uninstall it, Java can now be disabled in Internet Explorer. See Microsoft Fix it to Disable Java in Internet Explorer.1) In the Java Control Panel, at minimum, set the security to high.
2) Keep Java disabled until needed. Uncheck the box "Enable Java content in the browser" in the Java Control Panel.

3) If you use Firefox or Pale Moon, install NoScript and only allow Java on those sites where it is required.
Instructions on removing older (and less secure) versions of Java can be found at http://java.com/en/download/faq/remove_olderversions.xml
References
- Java SE 8u71 Update Release Notes
- Java SE 8u72 Update Release Notes
- Java, The Never-Ending Saga
- Oracle Critical Patch Update Advisory
- Oracle Quality Assurance Blog
- Critical Patch Updates and Security Alerts

Remember - "A day without laughter is a day wasted."
May the wind sing to you and the sun rise in your heart...
Go to link Download
Sunday, May 7, 2017
Out of band release for Security Bulletin MS15 078
Out of band release for Security Bulletin MS15 078

Microsoft released out-of-band critical security update which addresses a vulnerability in Microsoft font driver that could allow remote code execution.
The vulnerability affects all supported versions of Microsoft Windows. A restart is required in order to apply the update.
Critical:
- MS15-078 --Vulnerability in Microsoft Font Driver Could Allow Remote Code Execution (3079904).
This security update resolves a vulnerability in Microsoft Windows. The vulnerability could allow remote code execution if a user opens a specially crafted document or visits an untrusted webpage that contains embedded OpenType fonts.
References
- MSRC: Out-of-band release for Security Bulletin MS15-078
- TechNet: Microsoft Security Bulletin MS15-078 - Critical
Remember - "A day without laughter is a day wasted."
May the wind sing to you and the sun rise in your heart...

Remember - "A day without laughter is a day wasted."
May the wind sing to you and the sun rise in your heart...
Go to link Download
Friday, April 28, 2017
Oracle Java Quarterly Security Update October 2015
Oracle Java Quarterly Security Update October 2015
Oracle released the scheduled critical security updates for its Java SE Runtime Environment software along with a subsequent update that includes "bug fixes".
Unwanted "Extras"
Although most people do not need Java on their computer, there are some programs and games that require Java. In the event you need to continue using Java, How-to Geek discovered a little-known and unpublicized option in the Java Control Panel to suppress the offers for the pre-checked unwanted extras that Oracle has long included with the updates. Although the Ask Toolbar has been removed, tha does not preclude the pre-checked option for some other unnecessary add-on.Do the following to suppress the sponsor offers:
- Launch the Windows Start menu
- Click on Programs
- Find the Java program listing
- Click Configure Java to launch the Java Control Panel
- Click the Advanced tab and go to the "Miscellaneous" section at the bottom.
- Check the box by the “Suppress sponsor offers when installing or updating Java” option and click OK.
Windows XP
For information on Java support for Windows XP, organizations and individuals who must continue using Windows XP and have Java installed are referred to the Oracle blog post, The future of Java on Windows XP (Henrik on Java).Update
If Java is still installed on your computer, it is recommended that this update be applied as soon as possible due to the threat posed by a successful attack.Download Information
Download link: Java SE 8u65Java SE 8u66 can be found here. Select the appropriate version for your operating system.
Verify your version: http://www.java.com/en/download/testjava.jsp
Notes:
- UNcheck any pre-checked toolbar and/or software options presented with the update. They are not part of the software update and are completely optional.
- Starting with Java SE 7 Update 21 in April 2013, all Java Applets and Web Start Applications should be signed with a trusted certificate. It is not recommended to run untrusted/unsigned Certificates. See How to protect your computer against dangerous Java Applets
Critical Patch Updates
For Oracle Java SE Critical Patch Updates, the next scheduled dates are as follows:- 19 January 2016
- 19 April 2016
- 19 July 2016
- 18 October 2016
Java Security Recommendations
For those people who have desktop applications that require Java and cannot uninstall it, Java can now be disabled in Internet Explorer. See Microsoft Fix it to Disable Java in Internet Explorer.1) In the Java Control Panel, at minimum, set the security to high.
2) Keep Java disabled until needed. Uncheck the box "Enable Java content in the browser" in the Java Control Panel.
3) If you use Firefox or Pale Moon, install NoScript and only allow Java on those sites where it is required.
Instructions on removing older (and less secure) versions of Java can be found at http://java.com/en/download/faq/remove_olderversions.xml
References
- Java SE 8 Update Release Notes
- Java, The Never-Ending Saga
- Oracle Critical Patch Update Advisory
- Oracle Quality Assurance Blog
- Critical Patch Updates and Security Alerts
Remember - "A day without laughter is a day wasted."
May the wind sing to you and the sun rise in your heart...
Go to link Download
Sunday, April 16, 2017
Nokia Security Codes for Hard Reset Soft Reset etc
Nokia Security Codes for Hard Reset Soft Reset etc

• How to check the running applications on your S60 device: simply press the menu key for a second. You can move up and down to an application or close it with the ‘C’ key.
• How to spare space on the mobile’s memory: You can store your messages on the storage card this way: Go to message settings, other memory in use and choose your storage card instead of phone memory.
• Some symbian series 60 secret codes:
Display your IMEI number by pressing *#06#
Display your firmware version by pressing *#0000#
Display your Bluetooth address by pressing *#2820#
• How to reset your series 60 device
You can soft reset your device with the code *#7780# + security code {12345 if you didn’t change it} so that your device will be back to factory settings. Your personal data will not be erased.
You can hard reset your device with the code *#7370# + security code {12345 if you didn’t change it} so that your device will be as the first day-all data are deleted because the phone is formatted!
• If your phone is seriously crashed and won’t boot, you can perform the same hard reset this way:
Make sure your battery is fully charged
Backup your personal data to your computer or an MMC storage card.
Switch off your nokia 3250.
Press and hold 3 keys: green dial key, * star key, no. 3 key on keypad and then press the power on/off to switch on the nokia 3250. Remember, do not let go the 3. Press and hold keys until you see the formatting screen. After a few minutes when the process is over , your nokia 3250 will be back to the original delivered system.
Go to link Download
Thursday, April 13, 2017
New Adobe CRITICAL Security Updates Acrobat Pro and Reader 11 0 03
New Adobe CRITICAL Security Updates Acrobat Pro and Reader 11 0 03
-
[Updated 2013-05-21 @8:38 AM: I removed the paragraphs and image regarding a low resolution icon for Adobe Reader. What I had witnessed was, I have discovered, yet another bug in Apples Finder application. Ive witnessed the exact same phenomenon with other newly installed apps. Refreshing or relaunching the Finder removes the problem. Not good Apple! Apologies to Adobe.]
On schedule, Adobe has posted critical security updates of both Acrobat Pro and Reader. The download links are below.
Thankfully, Adobe has (belatedly) provided an updated Security Bulletin as well, which is also linked below. The updates patch 27 security vulnerabilities.
Security Bulletin:
http://www.adobe.com/support/security/bulletins/apsb13-15.html
Adobe Reader XI (11.0.03):
http://get2.adobe.com/reader/
Adobe Acrobat Pro XI (11.0.03):
http://www.macupdate.com/download/1833/AcrobatUpd11003.dmg
Here are the security CVE vulnerabilities patched by these updates:
These updates resolve memory corruption vulnerabilities that could lead to code execution (CVE-2013-2718, CVE-2013-2719, CVE-2013-2720, CVE-2013-2721, CVE-2013-2722, CVE-2013-2723, CVE-2013-2725, CVE-2013-2726, CVE-2013-2731, CVE-2013-2732, CVE-2013-2734, CVE-2013-2735, CVE-2013-2736, CVE-2013-3337, CVE-2013-3338, CVE-2013-3339, CVE-2013-3340, CVE-2013-3341).
These updates resolve an integer underflow vulnerability that could lead to code execution (CVE-2013-2549).
These updates resolve a use-after-free vulnerability that could lead to a bypass of Adobe Readers sandbox protection (CVE-2013-2550).
These updates resolve an information leakage issue involving a Javascript API (CVE-2013-2737).
These updates resolve a stack overflow vulnerability that could lead to code execution (CVE-2013-2724).
These updates resolve buffer overflow vulnerabilities that could lead to code execution (CVE-2013-2730, CVE-2013-2733).
These updates resolve integer overflow vulnerabilities that could lead to code execution (CVE-2013-2727, CVE-2013-2729).
These updates resolve a flaw in the way Reader handles domains that have been blacklisted in the operating system (CVE-2013-3342).

--
Go to link Download
Monday, April 10, 2017
Norton Antivirus Internet Security dan 360 2014
Norton Antivirus Internet Security dan 360 2014

LINK DOWNLOAD :
DIRECT LINK OEM DOWNLOAD NORTON INTERNET SECURITY & 360
FREE DOWNLOAD NORTON INTERNET SECURITY OEM (90 DAYS)
NORTON ANTIVIRUS 2014
Go to link Download
Panda Internet Security 2013 18 01 01
Panda Internet Security 2013 18 01 01
 |
| Panda Internet Security 2013,panda internet security 2013,panda internet security 2013 review,panda internet security 2013 free trial,panda internet security 2013 system requirements,panda internet security 2013 s,panda internet security 2013 c,panda internet security 2013 kn,panda internet security 2013 ac,panda internet security 2013 download,panda internet security 2013 free download |
Panda Internet Security allows you to use the Internet for anything, like shopping and banking online, with total peace of mind. It protects you from viruses, hackers, online fraud, identity theft and all the other known and unknown threats.
In addition, it keeps your inbox spam-free, and allows you to browse the web privately and securely with the new Panda Safe Browser. Parental Control allows your children can browse the Internet safely.
More security, more protection. More protection: Collective Intelligence is a network of information based on the community of users where we all share and contribute knowledge.
More speed, more simplicity. Lighter and easier: In addition to being very easy to use, it uses our Collective Intelligence, hosted on the Internet instead of your PC, that results in minimum performance impact on your PC.
More complete than ever. More than a simple Internet Security: Includes a set of new tools for your total piece of mind, protection and productivity.
In addition, it keeps your inbox spam-free, and allows you to browse the web privately and securely with the entirely new Panda Safe Browser. With the Parental Control, your children can browse the Internet safely.
Here are some features of Panda Internet Security:
Panda Internet Security 2013,panda internet security 2013,panda internet security 2013 test,panda internet security 2013 k,panda internet security 2013 ke,panda internet security 2013 deinstallieren,panda internet security 2013 windows 8,panda internet security 2013 aktivierungsco,panda internet security 2013 se,panda internet security 2013 full download
Protection against spyware:
· Protects your privacy by preventing spyware from being installed on your computer. The anti-spyware protection prevents this type of software from compiling data about your Internet habits and preferences.
Protection against unknown threats:
· Thanks to the revolutionary TruPrevent Technologies now, more than ever, you will be protected against malware at all times.
Protection against all types of malware:
· Not only are you protected against viruses. Now you have integrated protection capable of combating all types of malicious software: hacking tools, jokes, malicious cookies, viruses, etc.
Maintenance:
· Make backup copies of your most valued documents to avoid losing them in the event of disasters. You can make backup copies of your documents easily in the location you choose: USB removable drives, CDs, DVDs, or even Internet secure servers.
Firewall:
· Neutralizes network viruses and prevents possible intrusions or attacks by hackers trying to enter your computer through the Internet.
Anti-spam filter:
· Protects you against junk mail, saving time and resources. The anti-spam protection will keep your inbox free from junk mail sent massively across the Internet.
Identity protection:
· Protects you against the growing number of fraud attempts on the Internet. For example, you can avoid spoof bank/financial service Web pages that are really controlled by fraudsters.
· Your passwords and credit card numbers will now be safer then ever. None of this data can leave you computer without your prior consent.
· If you connect to the Web via modem, you wont have to worry about calls being made to premium-rate numbers without your consent.
Web content filtering:
· If your computer is used by other people, you can put restrictions on the content they can access on the Internet. Configure the filters for each user and you wont have to worry about some users accessing inappropriate content.
Protection against vulnerabilities:
· Protects you against security holes in certain applications that could make your computer easy prey to all types of malicious software and hackers. Now you can fix vulnerabilities detected in your computer, giving you even greater security.
Requirements:
· Processor: Pentium 300 MHz or faster
· RAM: 128 MB without TruPrevent Technologies, 512 MB with TruPrevent Technologies (1 GB recommended)
· Hard Disk: 275 MB free space
· MS Internet Explorer 6.0
· CD-ROM drive
Limitations:
· 30 days trial
· Nag screen
Whats New in This Release:
· IMPROVED! Protection against all types of malware - Protects you in real time against all types of known and unknown malware, thanks to the knowledge gathered from the panda Community.
· Collective Intelligence - A new threat is identified and in a matter of seconds all Panda Security’s customers worldwide are protected.
· Personal Firewall - Firewall with WiFi security that blocks intruders and hackers, even in your wireless network.
· IMPROVED! Panda USB Vaccine - Panda USB Vaccine protects your PC and USB drive from infection.
· NEW! Virtual Keyboard - Write your password in a safe way thanks to the Virtual Keyboard.
· PLUS! Panda Safe Browser (Sandboxing) - Suspecting that a web is dangerous? Access it without risk through the Save Browser (sandboxing).
· NEW! Multimedia/Gaming Mode - Enjoy the multimedia world and play without interruptions! Your antivirus keeps watching without bothering you.
· NEW! Home Network Manager - Checks the security status ...
Panda Internet Security 2013,panda internet security 2013,panda internet security 2013 cr,panda internet security 2013 se,panda internet security 2013 download,panda internet security 2013 gratis,panda internet security 2013 kn,panda internet security 2013 opinioni,panda internet security 2013 li
Go to link Download
Saturday, April 8, 2017
Norton Internet Security 2016 Offline Installer Beta Download
Norton Internet Security 2016 Offline Installer Beta Download
Norton Internet Security 2016:
Go to link Download
Friday, April 7, 2017
Network Security
Network Security

Go to link Download
Tuesday, April 4, 2017
Norton Mobile Security Product Key APK Android App Free Download
Norton Mobile Security Product Key APK Android App Free Download
Norton Mobile Security Product Key works as a handy Android app for mobile security and virus protection for devices such as Smartphone and tablets.

Norton Mobile Security APK Crack Product Serial Key Key Activation Code Android App Free Download Full Version
It is such an outstanding tool that locks user’s devices remotely for prevention of data theft.Norton Mobile Security Antivirus App Features:
- It can sync all contacts and then share them all across many devices.
- Right after 10 failed attempts of unlocking, this Android app locks your device automatically.
- Through one website, you can control and monitor the protection of mobile devices.
- It scans and completely removes all those apps that have malware and viruses that can harm your android phone or device.
- Download Lookout Premium APK Cracked Free
- Antivirus Free Download For Mobile Security
- Download Mobile Security & Antivirus Free
- Download Antivirus Booster And Cleaner App Free
- Free Download Avast Mobile Security & Antivirus APK
Go to link Download
Saturday, April 1, 2017
One Click Security Application Downloader SSDownloader
One Click Security Application Downloader SSDownloader
New threats and viruses are appearing everyday,so its important that the database be updated on a regular basis.So every computer user have to make sure that his anti-virus database gets checked daily.In addition to that you need various tools to secure you PC like Antispyware,Firewall ,Antimalware and other utility tools.Such software makers updated their product periodically .Updating your security software is not easy for you regularly.It is useful , if there is one click security application downloader available to combine all popular anti virus, firewalls and anti malware applications under one application to download.
SSDownloader comes to rescue you - an open source app which makes downloading current versions of popular Antivirus, Antimalware, Firewall, and Utility software a snap. This portable has a very simple user interface in which users select the security packages they wish to use. It automatically refreshes its database and all software packages in the system are completely legal and free to use.
Free security applications Included are popular free tools like Avast!, MS Security Essentials, Malwarebytes, HiJack This, Comodo Firewall, CCleaner, AutoRuns, Process Explorer and more.

SSDownloader is very useful to save our time for searching security application around the Internet and also excellent way to make sure youve always got up-to-date installers at the ready.
Features:
- Download the most popular free and paid security software with only one click.
- Don’t worry about OS or 32bit/64bit, the right version will be automatically downloaded.
- Stay up to date, always newest versions of the software will be downloaded.
- Just choose what you want to download and you will see a notification as soon your downloads finished
Download: SSDownloader | Opensource |1.37MB | Windows XP,Vista,7
Go to link Download
Oracle Java Critical Security Update
Oracle Java Critical Security Update
Oracle released the scheduled critical security updates for its Java SE Runtime Environment software.
This is a Critical Patch Update that affects Oracle Java SE, versions 5.0u71, 6u81, 7u67, 8u20. From The Assurance Blog:
"Out of the 154 vulnerabilities fixed with today’s Critical Patch Update release, 31 are for the Oracle Database. All but 3 of these database vulnerabilities are related to features implemented using Java in the Database, and a number of these vulnerabilities have received a CVSS Base Score of 9.0."
Unwanted "Extras"
Oracle has long included pre-checked options with the updates. Although most people do not need Java on their computer, there are some programs and games that require Java. In the event you need to continue using Java, How-to Geek discovered a little-known and unpublicized option in the Java Control Panel to suppress the offers for the pre-checked unwanted extras.- Launch the Windows Start menu
- Click on Programs
- Find the Java program listing
- Click Configure Java to launch the Java Control Panel
- Click the Advanced tab and go to the "Miscellaneous" section at the bottom.
- Check the box by the “Suppress sponsor offers when installing or updating Java” option and click OK.
Windows XP
There has been a lot of recent controversy regarding Java updates for Windows XP. While Windows XP has reached end of life, Java 7 will continue to be updated until April, 2015.Thus, organizations and individuals who must continue using Windows XP and have Java installed can also continue getting updates for Java 7. It is noted, however, that if an issue arises that is specific to Windows XP, Oracle is not required to and also may not be able to create a patch. For additional information, refer to the Oracle blog post, The future of Java on Windows XP (Henrik on Java).
Update
If Java is still installed on your computer, it is recommended that this update be applied as soon as possible due to the threat posed by a successful attack.Download Information
Download link: Java SE 8u25Verify your version: http://www.java.com/en/download/testjava.jsp
Notes:
- UNcheck any pre-checked toolbar and/or software options presented with the update. They are not part of the software update and are completely optional.
- Starting with Java SE 7 Update 21 in April 2013, all Java Applets and Web Start Applications should be signed with a trusted certificate. It is not recommended to run untrusted/unsigned Certificates. See How to protect your computer against dangerous Java Applets
Critical Patch Updates
For Oracle Java SE Critical Patch Updates, the next scheduled dates are as follows:- 20 January 2015
- 14 April 2015
- 14 July 2015
- 20 October 2015
Java Security Recommendations
For those people who have desktop applications that require Java and cannot uninstall it, Java can now be disabled in Internet Explorer. See Microsoft Fix it to Disable Java in Internet Explorer.1) In the Java Control Panel, at minimum, set the security to high.
2) Keep Java disabled until needed. Uncheck the box "Enable Java content in the browser" in the Java Control Panel.
 |
| (Image via Sophos Naked Security Blog) |
3) If you use Firefox, install NoScript and only allow Java on those sites where it is required.
Instructions on removing older (and less secure) versions of Java can be found at http://java.com/en/download/faq/remove_olderversions.xml
References
- Java SE 8 Update Release Notes
- Java, The Never-Ending Saga
- Oracle Quality Assurance Blog
- Oracle Critical Patch Update Advisory October 2014
- Oracle Critical Patch Advisory
Remember - "A day without laughter is a day wasted."
May the wind sing to you and the sun rise in your heart...
Go to link Download
Thursday, March 30, 2017
Norton Internet Security 2016 Serial Key Lifetime Download
Norton Internet Security 2016 Serial Key Lifetime Download
Norton Internet Security 2016 Serial Key Lifetime Free Downlod


Norton Internet Security 2016 Latest Features:
Go to link Download
Tuesday, February 28, 2017
Norton Antivirus and Internet Security 2014 v21 2 0 38 FREE DIRECT DOWNLOAD LINK
Norton Antivirus and Internet Security 2014 v21 2 0 38 FREE DIRECT DOWNLOAD LINK


Go to link Download
Sunday, February 26, 2017
Oracle Java Quarterly Security Updates July 2015
Oracle Java Quarterly Security Updates July 2015
Oracle released the scheduled critical security updates for its Java SE Runtime Environment software.
Unwanted "Extras"
Although most people do not need Java on their computer, there are some programs and games that require Java. In the event you need to continue using Java, How-to Geek discovered a little-known and unpublicized option in the Java Control Panel to suppress the offers for the pre-checked unwanted extras that Oracle has long included with the updates. Although the Ask Toolbar has been removed, tha does not preclude the pre-checked option for some other unnecessary add-on.Do the following to suppress the sponsor offers:
- Launch the Windows Start menu
- Click on Programs
- Find the Java program listing
- Click Configure Java to launch the Java Control Panel
- Click the Advanced tab and go to the "Miscellaneous" section at the bottom.
- Check the box by the “Suppress sponsor offers when installing or updating Java” option and click OK.
Windows XP
For information on Java support for Windows XP, organizations and individuals who must continue using Windows XP and have Java installed are referred to the Oracle blog post, The future of Java on Windows XP (Henrik on Java).Update
If Java is still installed on your computer, it is recommended that this update be applied as soon as possible due to the threat posed by a successful attack.Download Information
Download link: Java SE 8u51Verify your version: http://www.java.com/en/download/testjava.jsp
Notes:
- UNcheck any pre-checked toolbar and/or software options presented with the update. They are not part of the software update and are completely optional.
- Starting with Java SE 7 Update 21 in April 2013, all Java Applets and Web Start Applications should be signed with a trusted certificate. It is not recommended to run untrusted/unsigned Certificates. See How to protect your computer against dangerous Java Applets
Critical Patch Updates
For Oracle Java SE Critical Patch Updates, the next scheduled dates are as follows:- 20 October 2015
- 19 January 2016
- 19 April 2016
Java Security Recommendations
For those people who have desktop applications that require Java and cannot uninstall it, Java can now be disabled in Internet Explorer. See Microsoft Fix it to Disable Java in Internet Explorer.1) In the Java Control Panel, at minimum, set the security to high.
2) Keep Java disabled until needed. Uncheck the box "Enable Java content in the browser" in the Java Control Panel.
3) If you use Firefox or Pale Moon, install NoScript and only allow Java on those sites where it is required.
Instructions on removing older (and less secure) versions of Java can be found at http://java.com/en/download/faq/remove_olderversions.xml
References
- Java SE 8 Update Release Notes
- Java, The Never-Ending Saga
- Oracle Quality Assurance Blog
- Critical Patch Updates and Security Alerts
Remember - "A day without laughter is a day wasted."
May the wind sing to you and the sun rise in your heart...
Go to link Download
Thursday, February 2, 2017
Oracle Java Quarterly Security Update Released
Oracle Java Quarterly Security Update Released
Oracle released the scheduled critical security updates for its Java SE Runtime Environment software.
It is important to also note that this release will be the last Oracle JDK 7 publicly available update. For more information, and details on how to receive longer term support for Oracle JDK 7, please see the Oracle Java SE Support Roadmap.
Unwanted "Extras"
Oracle has long included pre-checked options with the updates. Although most people do not need Java on their computer, there are some programs and games that require Java. In the event you need to continue using Java, How-to Geek discovered a little-known and unpublicized option in the Java Control Panel to suppress the offers for the pre-checked unwanted extras.- Launch the Windows Start menu
- Click on Programs
- Find the Java program listing
- Click Configure Java to launch the Java Control Panel
- Click the Advanced tab and go to the "Miscellaneous" section at the bottom.
- Check the box by the “Suppress sponsor offers when installing or updating Java” option and click OK.
Windows XP
For information on Java support for Windows XP, organizations and individuals who must continue using Windows XP and have Java installed are referred to the Oracle blog post, The future of Java on Windows XP (Henrik on Java).Update
If Java is still installed on your computer, it is recommended that this update be applied as soon as possible due to the threat posed by a successful attack.Download Information
Download link: Java SE 8u45Verify your version: http://www.java.com/en/download/testjava.jsp
Notes:
- UNcheck any pre-checked toolbar and/or software options presented with the update. They are not part of the software update and are completely optional.
- Starting with Java SE 7 Update 21 in April 2013, all Java Applets and Web Start Applications should be signed with a trusted certificate. It is not recommended to run untrusted/unsigned Certificates. See How to protect your computer against dangerous Java Applets
Critical Patch Updates
For Oracle Java SE Critical Patch Updates, the next scheduled dates are as follows:- 14 April 2015
- 14 July 2015
- 20 October 2015
- 19 January 2016
Java Security Recommendations
For those people who have desktop applications that require Java and cannot uninstall it, Java can now be disabled in Internet Explorer. See Microsoft Fix it to Disable Java in Internet Explorer.1) In the Java Control Panel, at minimum, set the security to high.
2) Keep Java disabled until needed. Uncheck the box "Enable Java content in the browser" in the Java Control Panel.
|
| (Image via Sophos Naked Security Blog) |
3) If you use Firefox or Pale Moon, install NoScript and only allow Java on those sites where it is required.
Instructions on removing older (and less secure) versions of Java can be found at http://java.com/en/download/faq/remove_olderversions.xml
References
- Java SE 8 Update Release Notes
- Oracle Critical Patch Update - January 2015
- Java, The Never-Ending Saga
- Oracle Quality Assurance Blog
- Critical Patch Updates and Security Alerts
Remember - "A day without laughter is a day wasted."
May the wind sing to you and the sun rise in your heart...
Go to link Download
Wednesday, January 25, 2017
Outpost Security Suite Pro 7 5 Full Version
Outpost Security Suite Pro 7 5 Full Version
Outpost Security Suite Pro has robust combination of advanced security technology which includes the best firewall in the industry of Outpost Firewall Pro, fast and effective Anti-malware, personalized Anti-spam and proactive Host Protection module .

Features
- Virus Bulletin VB100 certified virus and spyware protection
- Preemptive protection secures against new and unknown threats
- Minimal impact on system performance
- Secured network and web connections
- Fast, safe and private web browsing
- Automatic configuration (Auto-Learn and cloud-based Improve Net)
- Subsequent malware scans up to 10 times faster
- Intuitive security decision-making
- Bulletproof self-defense
- Real-time monitoring of security-related activities and events
- Minimal hardware requirements
- Entertainment mode for uninterrupted games and streaming video
Outpost Security Suite v7.5.1 Pro edition is normally priced $44.95 per 2 year license. Visit here to grab free serial registration key code to activate Outpost Security.Enter the promotional code given below along with your name & email id
Promo Code:54YP8-BPAWD-GK48G-KWGC8-GCC4C

Copy & paste the serial key code provided from the next page to activate the software

Download Outpost 7.5 Setup (32-bit) | Download Outpost v7.5 Setup (64-bit)
Go to link Download
Wednesday, January 4, 2017
Ongoing Crazy Security Issues Nothing Much And Too Much To Say
Ongoing Crazy Security Issues Nothing Much And Too Much To Say
INTRODUCTION
There are a great many computer security issues going on these days. The increase in ongoing security issues over this past spring and summer could be called an ongoing explosion of mushroom cloud proportions. The number of ongoing issues is quite literally overwhelming. As a computer security watcher, researcher, analyzer, commentator and teacher, Im intimidated by having so much to comprehend.
Should I be writing about all of this within the context of this my Macintosh Security blog?
Because of my manifesto for this blog, my answer is no. I wish to write here only about directly dangerous issues to Apple computer users. I also wish to write articles that provide useful information, summaries and teaching Apple computer users. I have no interest in being redundant to other peoples blog work on the Internet, except in an effort to bring their work to the attention of others. I also focus what I write here at average Apple computer users. My goal is to take the complicated and translate it into information that can be both comprehended and used by average Apple computer users. Let folks like me comb through the, frankly chaotic, world of geek level information and summarize it down into something readable by mere humans.
WHAT TO SAY WHEN THERES NOTHING MUCH AND TOO MUCH TO SAY
Without directly helpful information to share, despite the exploding mushroom cloud of ongoing computer security issues, I say nothing. I do this because I despise FUD! Needless FEAR, UNCERTAINTY and DOUBT are worthless. Theyre used a methods of manipulation and propaganda. These nasty tools are used to drive we humans into a state of despair and desperation, what I call Desperation Mode whereby we will blunder our way into actions that suit the manifestos of the scum humans who are manipulating them. I have zero interest in playing these self-destructive, disrespectful games.
Therefore, when the only affect of my writing would be to create FUD, I dont write. Im very happy to rip the mask off off FUD! Im pleased when I can point out and satirize FUD. But I never see a point in messing up others by making my own FUD.
However, I believe it is useful to at least point out whats going on in the background while I wait for something useful to provide here in the blog. Theres nothing much to say, but heres whats cooking:
WHAT COOKING ON THE APPLE COMPUTER SECURITY STOVE?
Its difficult to create a priority list regarding these subjects. Whats more important? Whats a more imminent problem? So Im not going to bother. Im simply going to list them as I see fit in the moment.
Oracles Internet Browser Java Plug-in:
Java remains the single most dangerous software you can run via the Internet. If you dont need to, then dont. Uninstall the Java Plug-in. Only install the Java plug-in if you run into a website that requires you to use it. Even then, use Java security features in your web browsers as well as Java security add-ons. Apple has made the most recent versions of Safari extremely save against abusive Java code. Its not perfect. Using the features can be intimidating and dysfunctional. But they are entirely worth using. I strongly suggest reading up on Safaris new Java control preference features as well as similar features in other browsers. I may provide my own write up about these settings in the future.
One good change I can point to is Oracles ongoing efforts to babysit Java by informing users when their installed version of the Java Plug-in is out-of-date. This is no substitute of the sandboxing of Java, as was originally intended by Javas creators Sun Microsystems. Buts its better than letting nasty little brat Java run around without a nanny to swat it when its being naughty.
Adobes Reader, Flash, AIR and Shockwave software:
Adobes Internet freeware remains the second most dangerous software you can run on the Internet. If you dont need to use it, then dont. Instead, uninstall it. Only install Adobes freeware if you run into website that requires you to us it. Even then, use Adobe plug-in security features in your web browsers as well as Adobe plug-in security add-ons. At this point, these features are no longer intimidating or dysfunctional. In general, they work quite well and are entirely worth using! Read up on the Adobe plug-in control preference features available within web browsers if you have questions about what theyre doing.
I personally cannot stand the invasiveness of Adobes update notification and installation features. Instead, as an advanced Mac user, I keep up with available updates on my own. Doing the same is a lot to ask of average Mac users. Therefore, it may well be best to allow Adobes root level Launch Agent to run on your system so it can help keep you up-to-date. Its up to the user to choose what to do. Adobes update notification is available in their installers if youd like to use it.
Heartbleed Bug:
Ive written up a couple articles about the dangerous and ongoing problems with old implementations of OpenSSL. This problem is going to live on for years, not kidding. Its entirely curable! However, oblivious, careless and lazy server administrators arent bothering. Therefore, this problem periodically does damage. There are now convenient hacker tools to take advantage of Heartbleed. They are scripted. You get them running, walk away, come back later and analyze the successfully harvested data. There are also analysis tools to help hackers patch together the 64-bit chunks of harvested data into a completed puzzle. If that puzzle contains exploitable user data, it is either exploited by the hacker or posted online for sale to crooks. The exploitable data can include anything from your mothers maiden name to a victims card numbers and PIN.
Every single Internet server containing the Heartbleed Bug has now been documented. If an Internet server administrator does not know if their server is exploitable, they should be fired or sued in civil court. I strongly expect such lawsuits to begin appearing this coming year. Its all about responsibility.
Bash Shell ShellShock Bugfest:
This is, for the moment, a dangerous problem for those running OS X servers that are directly exposed to the Internet. If youre behind a router, you are probably safe in the short term. I know full well that eventually there will be PWNing (owning, taking over or zombieing) of routers and OS X client users. Ill address those exploits if or when they become evident. For now, only OS X Internet servers are at risk.
Describing this problem is a challenge because in and of itself it is turning into a mushroom cloud of security flaws. Ill simply say that Bash (Bourne-again shell) is a UNIX shell used by OS X, OS X applications and OS X users to access CLI (character line interface) applications that are installed in the OS X system. It is old, poorly vetted, incredibly insecure software. Oddly, its numerous security flaws were unknown, at least in public, for many years. Over the past few days, the report of one single security bug in Bash has lead to the revelation that Bash has an undetermined plethora of security bugs. So far, I know of two security updates for Bash that have been made available over the past few days. But they do NOT solve the ongoing revelations of further security flaws.
The result is that Bash itself is not fit for use on servers exposed to the Internet. The result, at the moment, is a debate and study of either:
1) Playing whack-a-mole by daily patching Bash as each new security flaw is discovered.
OR
2) Using an adequate replacement of the Bash shell.
OR
3) Taking affected servers OFF the Internet until a full and final solution is developed.
Meanwhile: Bash Internet exploit tools have already been made available to hackers, and theyre being used.
Replacing Apples installed version of the Bash shell is a huge PITA unless you understand exactly why and what youre doing. I cannot recommend bothering with it unless youre an advanced user who knows how to use the CLI to run their Mac. It is such a huge PITA the I have consistently run into Mac computer geeks who have posted WRONG and INCOMPLETE instructions for replacing Apples Bash shell. When the geeks cant get it right, no way should average Mac users touch it.
Thankfully, as I indicated above, no average Mac users need bother to worry about the Bash shell security flaws affecting their computer. Only OS X server administrators need worry about it, for now. This may well change! If the Bash problems arent solved in a hurry, there will no doubt be related attacks on average users routers and Trojan horses to abuse their Macs, if not outright PWN them. Thats a worry for another day, if it happens at all. Meanwhile, we sit and wait for the experts to thrash through the Bash source code and clean up the potentially catastrophic mess buried therein.
There are piles of ongoing, constantly going out-of-date articles about the Bash ShellShock bugs. Keeping up will drive you nuts. If youre that kind of person, be sure to read only the most up-to-date articles AND be sure to read from a variety of sources. Thats the only way to know whats actually going on at-the-moment. Bash analysis is constantly revealing new problems. New exploits are constantly showing up on the net.
Heres one very good overview, for today anyway, of the Bash ShellShock bugfest, posted by Intego:
http://www.intego.com/mac-security-blog/shellshock-vulnerability-what-mac-os-x-users-need-to-know/
Retail POS POS Device Malware:
"POS" has two meanings relevant to this problem. The first meaning is Point Of Sale regarding devices that are used to collect customer payment data, be they Chip and PIN card readers or magnetic strip card readers. (To be clear, if a POS device has this problem, using Chip and PIN solves nothing-at-all. Dont be fooled by claims to the contrary). The second meaning is an deliberate punning obscenity which Ill leave you to translate. I use this obscenity because these devices are an obscenity of bad technology.
This is another curable security problem that lazy, stupid, cheap retailers are NOT patching. The stupidity involved is stunning and beyond comprehension. From my point of view, this catastrophe fits perfectly into my concepts of bad biznizz. These are companies who literally dont give a rats about their customers, to say the least, to state the obvious. They dont know how to run their businesses. They are distinctly anti-capitalist in their attitudes and their obliviousness. Id like to be kind and say that these companies may only, innocently, be ignorant of the technology theyre using to enable their businesses. But that is NOT the case. They know exactly what technology theyre using and they are making the choice to IGNORE the requirements of owning and using that technology.
Ive previously written about the source of this problem. My quick summary is this:
1) These devices user Windows XP Embedded as their operating system.
2) Windows XP exposes all collected data in-the-clear (having no encryption) in RAM on these machines.
3) Hackers on the Internet search for and find routes by which they are able to BOT (aka PWN) all the POS devices networked within victim company. They also BOT at least one node server computer within the same network.
4) The malicious malware hacking onto these machines sits in wait, watching all the data revealed in RAM, then sends that data off to a server node within the network of the infected companies. The collected data is then sent over the Internet to the hacker bot wranglers out on the Internet.
5) The collected data is then analyzed. Personal data is extracted. This data includes everything read into the retail POS devices, including card numbers and PIN numbers. (Yes, this includes Chip and PIN card data).
6) This personal data is then either used or sold on the Internet to crooks.
After the initial catastrophic revelations of this problem, (thank you Target, Neiman Marcus, ad nauseam), security updates were provided by Microsoft to update these archaic Windows XP Embedded devices. The updates did NOT solve the problem of in-the-clear exposure of personal data in RAM. They wont be able to solve that problem! But these patches have at least been swatting at each specific variant of malware being used to PWN these POS devices.
Except, a great many companies are NOT updating their POS devices. This is inexcusable. This is irresponsible. This constitutes customer abuse, as future court cases will no doubt prove. And of course, this is bad biznizz. The biggest recent new revelation of PWNed POS devices and the subsequent sales of customer personal data over the Internet, has come from the willfully stupid company Home Depot. The latest figure I have read is that Home Depot literally gave away 56 MILLION customer card accounts. Unforgivable.
New revelations of retail POS POS device PWNing are happening at an incredible rate. These revelations are not stopping. The number of worthless companies who are ignoring this problem is incomprehensible. Everyone loses, from the companies to the banks to the disrespected customers. The only winners are the hacker crooks. And yet this problem is NOT abating.
Obviously, this problem has no direct impact on Apple computer users. It does impact every credit and debit card user, many of whom are Apple computer users. Therefore, its relevant here at this blog. Expect more of this curable security nightmare well on into the future.
The ultimate solution to in-the-clear data in RAM is end-to-end encryption. Were going to be hearing references to this concept also well on into the future until such time as it become the DEFAULT in the retail industry. And again: Chip and PIN cards do NOT solve this problem. They have nothing to do with it. Magnetic stripe cards have nothing to do with it. Insecure POS devices and bad biznizziz are the problem.
And so forth...
The above are the big ongoing problems. There are smaller problems as well, the most prominent of which is:
ADWARE. My colleague Thomas Reed is brilliantly covering the adware problem and has created a detection and removal tool AdwareMedic which I highly recommend! Ive been a beta-tester for Thomass adware tool and have been thoroughly impressed. If youve been the victim of adware, head over to Thomas The Safe Mac website for both documentation and the solution. Bravo Thomas!
Thomass The Safe Mac website covers many Apple computer security issues that I dont. Id check out Thomass site side-by-side with mine. Thomas maintains what we both consider the definitive list of both old and new Mac malware. Because Thomas and I belong to a great group of malware researchers and writers created by Mark Allen, the creator of the terrific ClamXav anti-malware, many of us on the Internet are coordinating our work and publications. Youll find all of these colleagues listed on the right side of this page under Friends of Mac-Security. I recommend the work of all of them.
For malware detection and removal I recommend that all Mac users check out and support ClamXav. Its donationware, free to download and use, well worth every installing on every Mac. It finds and removes the vast majority of not only Mac malware, but also Windows and Linux malware. Its a gem of the Mac community. ClamXav is available from the Apple App Store. I strongly suggest instead downloading it directly from Marks ClamXav website as that version includes efficient, non-invasive real-time malware scanning. This feature means you can automatically scan every file you download from the Internet. If you wish, you can aim ClamXavs real-time specifically at your Downloads folder, a terrific way to catch Trojan horses and break social engineering by malware rats. (Unfortunately, at this time Apple does not allow real-time scanning in apps offered at the App Store).
There are a number of excellent commercial anti-malware programs. My personal favorites are from Intego and Sophos. Many people prefer anti-malware from F-Secure and Avast. (I would have put Kaspersky AV in this list. But Eugene Kasperskys outrageous Mac security FUD mongering on his blog this week killed my enthusiasm dead. What a shill! What a Symantec-clone!)
[Update 2014-10-28: I added Avast to the preferred list above. My apologies for not putting it there in the first place. A good friend of mine considers Avast to have the best free anti-malware application available. My blunder: Confusing it with another free anti-malware app that was infesting victims with adware.]
There are also some awful anti-malware programs. I personally suggest staying away from, Symantecs Norton™ AntiVirus , PCTools iAntiVirus, and MacKeeper. Ive found these applications to generally be inadequate, buggy, out-of-date or outright abusive to users.
For detecting both legal and illegal spyware, any of the recommended commercial anti-malware programs can be useful. The MacScan shareware application specifically targets spyware. However, I have never been impressed by the thoroughness of its scans. Therefore, if you believe it might be useful, be sure to test it before buying it.
As usual, the very best overall advice I can offer is to:
1) Make A Backup! Its the #1 Rule of Computing. If you dont backup, you deserve what you get.
2) Keep Up-To-Date! This is particularly important for Apple software.
3) Before You Update OS X, be sure to:
- Repair your boot volume.
- Repair your boot volumes permissions.
(Yes, repair your permissions. Its not crucial, but it can be extremely useful).
Thus ends todays mind dump.
I hope you find this useful, versus merely mind-numbing.
:-Derek
Go to link Download